

Get 2021 Updated Free Palo Alto Networks PCNSA Exam Questions & Answer
PCNSA Dumps PDF and Test Engine Exam Questions
What Areas PCNSA Assesses You on?
There are six different domains covered under this certification exam. These areas and their details are as follows:
- Palo Alto Networks Cybersecurity Portfolio Core
First, this topic is concerned with identifying the components alongside operations targeting the architecture of Single-Pass Parallel Processing. In addition, candidates will learn more about Strata Security for organizations, Prismas Security for the Cloud, and Cortex Security Operational procedures. The next area to be covered here is centered on the stages of the lifecycle of a cyberattack as well as the firewall mitigations which are capable of preventing attacks. To finalize, this domain describes the Zero Trust model as well as traffic moving via networks.
- Securing Traffic
This objective covers risk scenarios and how the appropriate profile can be applied. Included here are threat logs, security profiles, and customization for antivirus, anti-spyware, vulnerability protection, URL filtering, and file blocking. Also, there is a safe search and HTTP header logging. The next part is about firewall protection against packet & protocol attacks. Included within this topic are protections like Denial-of-Service, zone, flood attack, SYN cookies, UDP, ICMP, reconnaissance attack, packet-based attack, etc. What comes after is how cloud DNS security can be used by the firewall in controlling domains based on traffic and how the PAN-DB database can be used by the firewall for controlling websites based on traffic. At last, in this section, candidates will get equipped with the knowledge of URL filtering components and how to monitor access to them.
- Identifying Users
The PCNSA exam also looks at user identification and maps different IP addresses for them. Additionally, it considers controlling access to particular URLs by utilizing custom filtering categories for URL and identifying the proper user ID agent to be deployed. Also, it connects to how the mapping of firewalls to user groups is done and the ID configuration options for users.
- Deployment Optimization
This topic engages the advantages as well as differences occurring between the PBA reports and Heatmap. In particular, it includes the Heatmap component that analyzes the deployment of Palo Alto Networks and filters the data by making use of various group devices. To know more, this area also covers the feature section for Zone mapping, which helps you identify the best traffic to use by choosing the appropriate zone.
- Simply Passing Traffic
To start is the subsection on identifying and configuring management interfaces for the firewall. It covers access to the firewalls for Palo Alto Networks, steps to gaining access to firewall, methods for managing firewall, services for firewall, etc. Managing firewall features is next with a focus on configurations for candidates, running, last saved, saved name configuration snapshot, export and import device states, and more. There is also configuring internal as well as external services targeting account administration, administrative roles, authentication sequence, configuration logs, etc. What follows further is the domain of firewall interfaces that include Ethernet, Virtual, Layer 2, Tap, Layer 3, and aggregate. Some parts cover security zones and virtual routers while others focus on the function of specific types of security, followed by identifying and configuring conditions, logging options, security policies. Also, implicit in addition to explicit rules and security rule hit count are to be covered by the PCNSA test. Finally, are the matters of NAT solution implementation covering NAT types, configuring source NAT, and more.
- Traffic Visibility
Traffic visibility concerns rules for security and this covers application shifts, dependent applications, and implicit applications as well as determining them. Such a topic is also about application filters or groups, application characteristics, properties, timeouts, and tools for optimizing security policies. The last part concerns features for streamlining policy creation for App-ID such as application tags and dependencies and explicit app dependency resolution targeting workflows.
NEW QUESTION 43
An administrator notices that protection is needed for traffic within the network due to malicious lateral movement activity. Based on the image shown, which traffic would the administrator need to monitor and block to mitigate the malicious activity?
- A. branch office traffic
- B. perimeter traffic
- C. east-west traffic
- D. north-south traffic
Answer: C
NEW QUESTION 44
Given the screenshot what two types of route is the administrator configuring? (Choose two )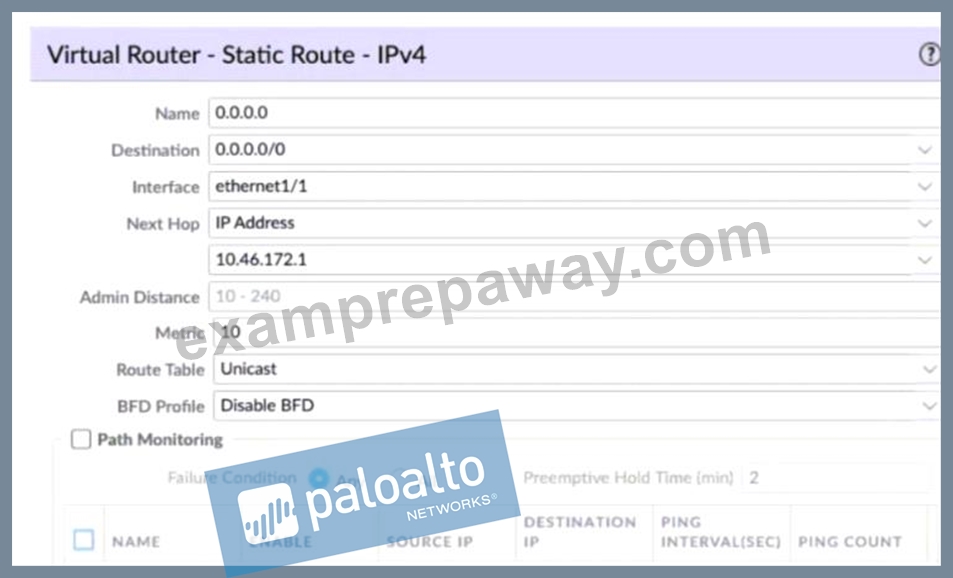
- A. OSPF
- B. default route
- C. BGP
- D. static route
Answer: B
NEW QUESTION 45
Given the image, which two options are true about the Security policy rules. (Choose two.)
- A. The Allow Office Programs rule is using an Application Group
- B. In the Allow FTP to web server rule, FTP is allowed using App-ID
- C. The Allow Office Programs rule is using an Application Filter
- D. In the Allow Social Networking rule, allows all of Facebook's functions
Answer: C,D
Explanation:
In the Allow FTP to web server rule, FTP is allowed using port based rule and not APP-ID.
NEW QUESTION 46 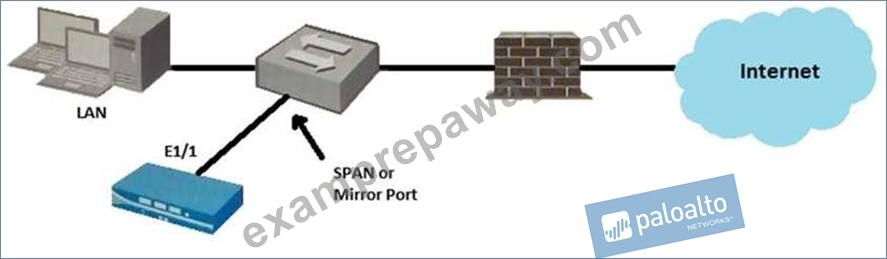
Given the topology, which zone type should interface E1/1 be configured with?
- A. Layer3
- B. Virtual Wire
- C. Tunnel
- D. Tap
Answer: D
Explanation:
Explanation/Reference:
NEW QUESTION 47
Which five Zero Trust concepts does a Palo Alto Networks firewall apply to achieve an integrated approach to prevent threats? (Choose five.)
- A. User identification
- B. Filtration protection
- C. Application identification
- D. Vulnerability protection
- E. Anti-spyware
- F. Antivirus
Answer: A,C,D,E,F
NEW QUESTION 48
Based on the graphic which statement accurately describes the output shown in the server monitoring panel?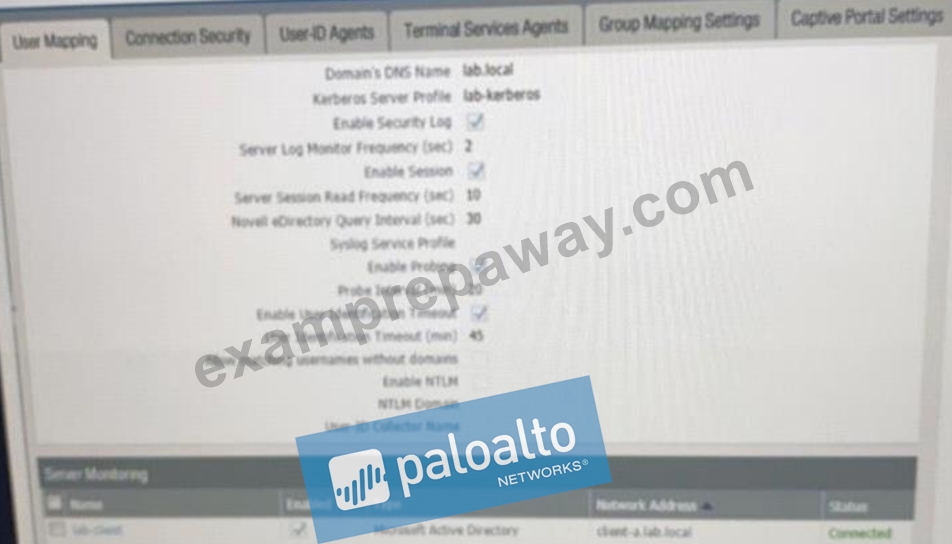

- A. The host lab-client has been found by a domain controller.
- B. The User-ID agent is connected to a domain controller labeled lab client.
- C. The host lab-client has been by the User-ID agent.
Answer: B
NEW QUESTION 49
Match the Cyber-Attack Lifecycle stage to its correct description.
Answer:
Explanation:
Explanation
Reconnaissance - stage where the attacker scans for network vulnerabilities and services that can be exploited.
Installation - stage where the attacker will explore methods such as a root kit to establish persistence Command and Control - stage where the attacker has access to a specific server so they can communicate and pass data to and from infected devices within a network.
Act on the Objective - stage where an attacker has motivation for attacking a network to deface web property
NEW QUESTION 50
Complete the statement. A security profile can block or allow traffic____________
- A. after it is matched by a security policy that allows traffic
- B. on unknown-tcp or unknown-udp traffic
- C. after it is matched by a security policy that allows or blocks traffic
- D. before it is matched by a security policy
Answer: A
Explanation:
Explanation
Security profiles are objects added to policy rules that are configured with an action of allow.
NEW QUESTION 51
Which administrator type utilizes predefined roles for a local administrator account?
- A. Dynamic
- B. Superuser
- C. Role-based
- D. Device administrator
Answer: A
NEW QUESTION 52
How is the hit count reset on a rule?
- A. with a dataplane reboot
- B. Device > Setup > Logging and Reporting Settings > Reset Hit Count
- C. in the CLI, type command reset hitcount <POLICY-NAME>
- D. select a security policy rule, right click Hit Count > Reset
Answer: D
NEW QUESTION 53
Given the topology, which zone type should zone A and zone B to be configured with?
- A. Layer2
- B. Tap
- C. Virtual Wire
- D. Layer3
Answer: D
NEW QUESTION 54
How often does WildFire release dynamic updates?
- A. every 30 minutes
- B. every 15 minutes
- C. every 60 minutes
- D. every 5 minutes
Answer: D
Explanation:
Explanation/Reference: https://docs.paloaltonetworks.com/pan-os/7-1/pan-os-new-features/wildfire-features/five-minute- wildfire-updates
NEW QUESTION 55
Which URL profiling action does not generate a log entry when a user attempts to access that URL?
- A. Override
- B. Allow
- C. Continue
- D. Block
Answer: B
NEW QUESTION 56
Which two settings allow you to restrict access to the management interface? (Choose two )
- A. enabling the Content-ID filter
- B. administrative management services
- C. restricting HTTP and telnet using App-ID
- D. permitted IP addresses
Answer: A,C
NEW QUESTION 57
Your company occupies one floor in a single building. You have two Active Directory domain controllers on a single network. The firewall's management plane is only slightly utilized.
Which User-ID agent is sufficient in your network?
- A. PAN-OS integrated agent deployed on the firewall
- B. Windows-based agent deployed on the internal network a domain member
- C. Windows-based agent deployed on each domain controller
- D. Citrix terminal server agent deployed on the network
Answer: C
Explanation:
Explanation/Reference: https://docs.paloaltonetworks.com/pan-os/8-1/pan-os-admin/user-id/map-ip-addresses-to-users/ configure-user-mapping-using-the-windows-user-id-agent/configure-the-windows-based-user-id-agent-for-user- mapping.html
NEW QUESTION 58
Which definition describes the guiding principle of the zero-trust architecture?
- A. never trust, always verify
- B. always connect and verify
- C. never trust, never connect
- D. trust, but verify
Answer: A
Explanation:
Explanation/Reference: https://www.paloaltonetworks.com/cyberpedia/what-is-a-zero-trust-architecture
NEW QUESTION 59
......
Verified PCNSA exam dumps Q&As with Correct 170 Questions and Answers: https://www.examprepaway.com/Palo-Alto-Networks/braindumps.PCNSA.ete.file.html
Get New PCNSA Certification – Valid Exam Dumps Questions: https://drive.google.com/open?id=1DFtgxWuJDLMvzlT_qdhshF08SZ4Eff4F